- 09/28/2026
- Posted by: Tri Smith, Instructor
- Category: Compliance
If you work in medical billing, coding, or any part of the healthcare revenue cycle, you handle protected health information every day. Understanding exactly what qualifies as PHI-and what does not-is one of the first skills any billing professional needs. This guide breaks down the legal definition, walks through the 18 HIPAA identifiers, and explains how PHI shows up in real billing workflows.
For a broader look at HIPAA compliance in billing, see MedicalBillingCourse.com’s guide to HIPAA for medical billers and data security for patients – this guide goes deeper specifically on what counts as PHI, which those broader pieces touch on but don’t cover in full.
Quick Answer: What Is PHI in Healthcare?
Protected health information (PHI) is any individually identifiable health information that is created or received by a covered entity or business associate. It relates to a person’s past, present, or future physical or mental health condition, the provision of health care, or payment for health care services-and it either identifies the person or could reasonably be used to identify them.
Here is what that means in practical terms:
-
PHI includes health information that identifies an individual, such as a diagnosis linked to a patient’s name on a claim form.
-
It covers all formats: paper records, electronic protected health information (ePHI), and verbal communication.
-
PHI is protected by the HIPAA privacy rule, which governs how covered entities and business associates use, share, and safeguard it.
-
HIPAA identifies 18 specific identifiers that, when combined with health or payment data, make information considered PHI.
-
PHI includes any information related to healthcare payment, from insurance claims to remittance advice.
Understanding what is considered PHI is essential for HIPAA compliance in medical billing, coding, and insurance workflows. At MedicalBillingCourse.com, students learn to recognize PHI in real billing scenarios-on CMS-1500 forms, EOBs, ERAs, and throughout the revenue cycle-rather than memorizing abstract definitions.
HIPAA Basics: Why PHI Exists in the First Place
Before covering what is PHI in more detail, it helps to know why the protection exists: the Health Insurance Portability and Accountability Act of 1996 was signed into law on August 21, 1996. Its goals included improving health insurance portability so workers could maintain coverage when changing jobs, reducing administrative waste in healthcare transactions, and establishing federal safeguards for individually identifiable health information. The Portability and Accountability Act addressed a gap: before HIPAA, there was no consistent federal standard for protecting patient data across healthcare providers, health plans, and health care clearinghouses.
Key milestones in how PHI protections developed:
-
December 2000: The Department of Health and Human Services published the final HIPAA privacy rule, establishing standards for protecting individually identifiable health information.
-
April 2003: Most covered entities-healthcare providers who transmit electronic claims, health plans, and clearinghouses-had to comply. Small health plans followed by April 2004.
-
April 2005: The HIPAA security rule took effect, adding technical safeguards specifically for ePHI.
-
2009–2013: The HITECH Act and subsequent Omnibus Rule expanded business associates’ direct liability and broadened the definition of PHI to include genetic information.
HIPAA regulations protect PHI from unauthorized disclosures, and covered entities must comply with the HIPAA privacy rule. Insurance portability and accountability are linked: patients can move between jobs and plans, and their personal health information must be protected across every system that touches it.
Formal Definition: How HIPAA Defines PHI
The formal answer to what is PHI comes from 45 CFR §160.103: PHI is a subset of individually identifiable health information created or received by covered entities and business associates. It must relate to a person’s health, health care, or payment for health care, and it must either identify the person or provide a reasonable basis for identification.
Three elements must be present simultaneously:
-
Health information: Diagnoses, treatments, lab results, medications, or payment details such as claims and insurance coverage.
-
Identifier: A data point (name, date, account number) that ties the health information to a specific person.
-
Held by a covered entity or business associate: The data must reside in a medical record or designated record set maintained by an entity subject to HIPAA.
PHI is created or received by healthcare providers or plans and includes health information linked to healthcare services. It covers past, present, or future physical or mental health conditions, treatment, and future payment for care. PHI also includes any information related to a healthcare service event or payment activity-from a single lab result to an entire billing record. Recognizing PHI at each stage is part of the full medical billing process walkthrough.
PHI vs PII: Personally Identifiable Information in a Healthcare Context
Understanding what is PHI versus PII starts with a broad category: names, Social Security numbers, electronic mail addresses, street address data, phone numbers, and similar details that can identify a person in any context. PII is not always considered PHI under HIPAA regulations. The difference is context and record location.
PII becomes PHI when it appears alongside health, treatment, or payment information in a designated record set maintained by a covered entity or business associate. PII can be protected if stored with PHI in a record set-but standing alone in a non-healthcare setting, it falls outside HIPAA’s scope.
|
Scenario |
Classification |
|---|---|
|
Email address in a clinic’s patient portal linked to appointment history |
PHI |
|
Same email address on a retail store’s marketing list |
PII only |
|
Patient name + diagnosis on a CMS-1500 claim |
PHI |
|
Employee name on a payroll spreadsheet with no health data |
PII only |
Some state and federal laws, including certain privacy act provisions, protect PII even when it is not considered PHI. But for billing professionals, the practical question is whether identifiers appear alongside health-related information in a record set connected to a covered entity.
The 18 HIPAA Identifiers: What Turns Health Data Into PHI
These 18 identifiers are central to what is PHI under HIPAA: the HIPAA privacy rule identifies 18 data elements-often called PHI identifiers-that must be removed to de-identify data under the Safe Harbor method. When any of these identifiers appear alongside health or payment details in a designated record set, the information is considered PHI.
The full list of PHI identifiers:
-
Names (patient, relatives, household members)
-
Geographical subdivisions smaller than a state (street address, city, county, zip code, and such geographic units)
-
All dates (except year) directly related to the individual: birth date, admission date, discharge date, date of death
-
Phone numbers
-
Fax numbers
-
Electronic mail addresses
-
Social Security numbers
-
Medical record numbers
-
Health plan beneficiary numbers
-
Account numbers
-
Certificate or license numbers (including license plate numbers)
-
Vehicle identifiers and serial numbers
-
Device identifiers and serial numbers
-
Web universal resource locators (URLs)
-
IP addresses
-
Biometric identifiers (including fingerprints and voice prints)
-
Full-face photographs and comparable images
-
Any other unique identifying number, characteristic, or code
Technology continues to evolve. Social media handles, metadata, and behavioral data can make individuals identifiable even when they are not explicitly listed among the original 18 identifiers-a growing concern as health data set usage expands.
What Is Considered PHI? Concrete Healthcare & Billing Examples
Information is considered PHI when it combines one or more of the 18 identifiers with health, treatment, or payment data in a record maintained by a covered entity or business associate.
Common examples in medical billing and coding:
-
A CMS-1500 claim form listing a patient’s name, street address, ICD-10 diagnosis codes, CPT procedure codes, and insurance member ID
-
An Explanation of Benefits (EOB) or Electronic Remittance Advice (ERA) showing services rendered, amounts paid, and patient demographic details
-
Eligibility verification responses tied to a member ID and health plan
-
Prior authorization documents containing a patient’s name, diagnostic information, and proposed treatment plan
-
Chart notes and lab results linked to a patient’s medical record number
Less obvious items that are also considered PHI:
-
A newborn’s photograph stored in the medical chart
-
A thank-you card scanned into the electronic health record
-
Demographic data on a patient intake form filed alongside clinical notes
-
A voicemail confirming a patient’s appointment for a mental health visit
If identifiers and health or payment data appear together in a billing record or medical record maintained by a covered entity, the information qualifies as PHI.
What Is Not Considered PHI Under HIPAA?
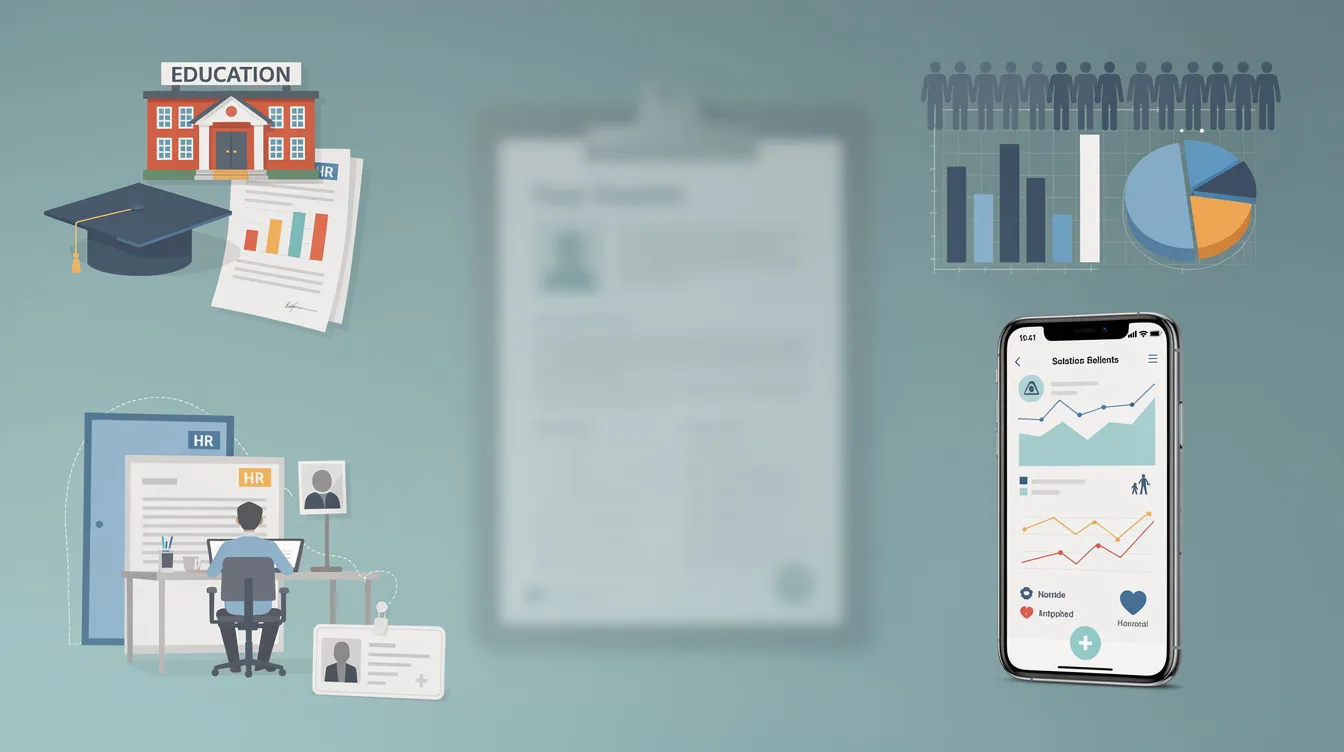
Not all health-related or identifying data falls under HIPAA’s protection. Context and where the data resides matter.
Examples of non-PHI:
-
De-identified health information: Data sets stripped of all 18 identifiers using the Safe Harbor method (or verified by an expert statistical method)
-
Employment records about sick days maintained purely as HR files, without clinical or health-related information
-
Education records protected by the Family Educational Rights and Privacy Act (FERPA)-these are generally outside HIPAA when held by educational institutions
-
Wellness app data stored by a company that is not a covered entity or business associate
-
Public health statistics aggregated so no individual can be identified
-
Information about individuals deceased for more than 50 years
Research health information stored only in a researcher’s files-never entered into a medical record or designated record set-may fall outside HIPAA, though other human subjects protections can apply. Entities that conduct research under institutional review boards follow separate frameworks.
Rule of thumb:
-
No covered entity involvement → not PHI
-
No health, treatment, or payment information → not PHI
-
No identifiers → not PHI
PHI Formats: Paper, Electronic (ePHI), and Verbal Information
Part of what is PHI under HIPAA is that it is format-neutral. HIPAA protects spoken, written, and electronic information alike, and PHI must be protected in all forms, including electronic.
Paper PHI:
-
Printed charts and progress notes
-
Superbills and CMS-1500 claim forms
-
Consent form copies with patient signatures
-
Photocopied insurance cards in patient files
-
Mailed EOBs
Electronic PHI (ePHI):
-
Electronic health record systems
-
Billing and practice management software
-
Clearinghouse transmissions (837/835 files)
-
Emails containing patient identifiers or clinical data
-
Cloud-stored backups, claim files sent via SFTP
Verbal PHI:
-
Hallway conversations referencing a specific patient’s condition
-
Voicemails containing appointment details or test results
-
Phone calls verifying insurance benefits using patient name and birth date
The HIPAA security rule applies specifically to ePHI, requiring technical safeguards like encryption and access controls. The HIPAA privacy rule applies across all PHI formats-paper, electronic, and verbal. Security rules work alongside privacy protections to create a layered compliance framework.
Designated Record Set & Medical Record: Where PHI “Lives”
Knowing where what is PHI actually lives starts with the designated record set: the group of medical and billing records a covered entity uses to make decisions about individuals. PHI must be maintained in a designated record set to fall under HIPAA’s protections and access requirements.
PHI can be a single scanned document or an entire medical record, as long as it resides within the designated record set. Covered entities may maintain multiple designated record sets-one for clinical patient care, another for billing-and PHI in any of them must be protected and made available when patients exercise their access rights.
Permitted Uses & Disclosures of PHI (Including Patient Consent)
Part of understanding what is PHI is knowing when it can be used: the HIPAA privacy rule applies strict controls to when PHI can be used or disclosed. Not every use requires patient consent or written authorization.
Uses permitted without written authorization (Treatment, Payment, and Healthcare Operations-TPO):
-
Sharing PHI between healthcare providers for continuity of patient care
-
Sending claims data to an insurer to obtain future payment
-
Internal auditing, quality improvement, and healthcare operations
-
Submitting documentation for prior authorization
Uses requiring formal written authorization:
-
Marketing communications using PHI
-
Sale of PHI
-
Most research uses outside of treatment context
Other disclosures allowed without authorization:
-
Public health reporting (disease surveillance, child abuse reporting)
-
Certain law enforcement requests
-
Workers’ compensation filings
-
Situations involving a serious threat to health or safety
-
Compliance investigation requests from regulators
Covered entities must provide a notice of privacy practices to patients, explaining how their individual’s health information may be used and disclosed. When disclosing PHI, the standard is to share only the minimum amount of information necessary to accomplish the purpose-billers should send only what the payer or recipient needs, not the entire chart.
Improper disclosures-sending PHI to the wrong fax number, including unnecessary clinical details-can trigger reportable breaches and penalties.
PHI, Business Associates & Medical Billing Workflows
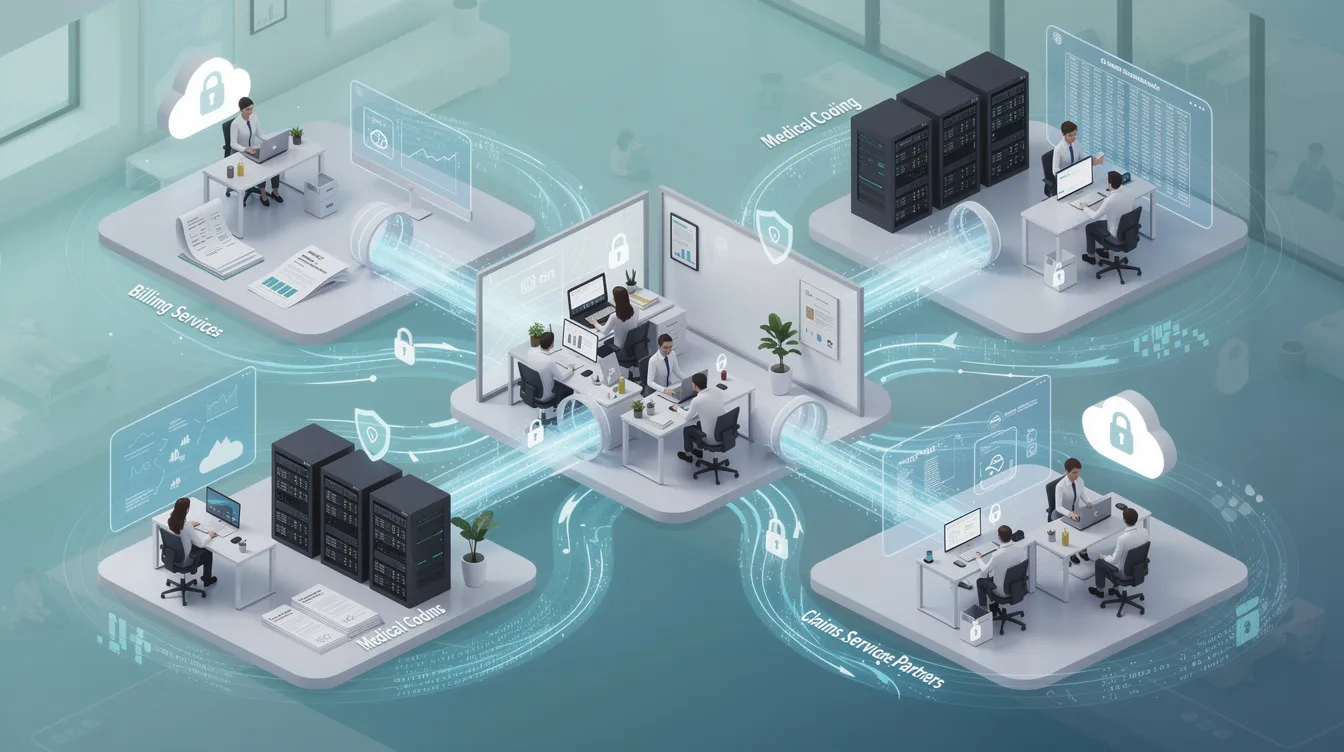
Business associates are central to what is PHI in practice: persons or entities that create, receive, maintain, or transmit PHI on behalf of a covered entity. In medical billing, business associates are everywhere.
Typical business associates in billing and coding workflows:
-
Independent medical billing companies
-
Coding and transcription services
-
Practice management and billing software vendors
-
Cloud storage and IT support providers with system access
-
Health care clearinghouses that process electronic claims
Business associates must sign Business Associate Agreements (BAAs) that outline safeguards, breach reporting duties, and permitted uses of PHI. After the 2013 Omnibus Rule, business associates have direct liability under HIPAA’s privacy and security rules. PHI handled by a business associate is protected identically to PHI held by the covered entity-a covered entity’s workforce and its vendors share accountability.
The scale of breach risk is significant and growing. Per HHS Office for Civil Rights breach reporting data, more than 7,600 large healthcare data breaches (affecting 500 or more individuals each) have been reported since mandatory reporting began in 2009, affecting over 1 billion individual records combined – a total driven sharply higher by a small number of very large incidents in recent years. Business associates are a significant and growing share of those reported breaches, which is exactly why BAAs and vendor oversight matter as much as a covered entity’s own internal safeguards.
In everyday billing workflows-claim submission, posting ERAs, working denials, verifying eligibility, communicating with payers-business associates routinely access PHI. MedicalBillingCourse.com’s training covers how to handle PHI correctly whether you work as an in-house biller or operate a home-based billing business under a BAA.
Protecting PHI: Practical HIPAA Compliance Tips for Billing & Coding
Once you know what is PHI, protecting it becomes the next priority: failing to protect PHI carries real consequences, financial penalties, loss of patient trust, and potential job loss. HIPAA regulations apply to every person who touches PHI, from front-desk staff to remote billing specialists.
Physical safeguards:
-
Lock file cabinets containing paper records
-
Keep printed claims and EOBs out of public view
-
Shred documents containing PHI before disposal
Technical safeguards for ePHI:
-
Use strong passwords and role-based access controls to restrict access to billing systems
-
Encrypt data in transit and at rest
-
Use secure Wi-Fi and VPNs for remote access
-
Patch software regularly and use HIPAA-compliant cloud services with signed BAAs
Administrative safeguards:
-
Complete ongoing HIPAA training
-
Follow clear policies enforcing the minimum necessary standard-share only the minimum amount needed
-
Establish procedures for reporting suspected breaches
-
Apply sanctions for improper access or disclosure
Common breach vectors to watch:
-
Phishing emails targeting staff with access to patient data
-
Lost or stolen laptops containing unencrypted ePHI
-
Misdirected faxes or emails sent to wrong phone numbers or addresses
Basic awareness prevents most incidents. MedicalBillingCourse.com’s certification programs incorporate HIPAA privacy and PHI handling into every step of revenue cycle training, so students build these habits from the start.
PHI, Patient Rights & Your Role as a Healthcare Professional
Beyond what is PHI itself, HIPAA gives patients specific rights over their protected health information. As a billing or coding professional, you will encounter these rights in day-to-day workflows.
Key patient rights:
-
Access: Individuals can request copies of their PHI. Individuals have the right to access their PHI within 30 days of a request, including electronic copies from an electronic health record where feasible.
-
Amendments: Individuals can request amendments to their PHI if they believe records are inaccurate or incomplete. Providers must respond with an approval or a written denial.
-
Accounting of disclosures: Individuals have the right to an accounting of disclosures-a record of certain times their PHI was shared over the past six years.
-
Restrictions: Individuals can request restrictions on PHI disclosures, such as limiting what is shared with a particular health plan.
-
Confidential communication: Patients may ask that communications be sent to an alternative street address, a P.O. Box, or by a specific method.
In billing, this plays out when you process record requests, flag amended diagnoses or procedure codes in the system, or document disclosures made during a compliance investigation or patient consent workflow. A patient’s preferred mailing address for correspondence may differ from their address on file, and billing staff need to honor these preferences.
Respecting PHI and patient rights is not only about avoiding penalties. It supports trust, accurate claims, and a smoother revenue cycle. MedicalBillingCourse.com’s 2026 Edition curriculum integrates these responsibilities into its certification programs, alongside the HIPAA Certification track for students who want to go deeper on compliance specifically.

Tri Smith is a Managing Partner and Instructor at MedicalBillingCourse.com, where he helps guide the program’s direction, curriculum, and student experience. With more than six years of experience, he focuses on practical medical billing skills, including claims, payer communication, compliance, and the full billing lifecycle.
Tri also helped lead the development of the 2026 course edition, including the Medical Billing and Coding certification track. His approach emphasizes clear instruction, practical application, and preparing students to apply what they learn in real-world billing environments.


